GDPR compliance requirements define how businesses must collect, use, store, and protect personal data. Companies that handle information belonging to people in the European Union must understand these rules, respect individual privacy rights, and follow the correct procedures. Failing to meet these obligations can lead to investigations, financial penalties, and loss of customer trust.
In September 2026, Ireland’s Data Protection Commission fined Google €403 million over its handling of users’ location data. The case highlights the importance of transparency and lawful data processing when businesses collect and use personal information.
This guide explains the key GDPR compliance requirements, the responsibilities businesses must meet, and the common challenges they may face. It also covers practical ways to strengthen data protection and reduce compliance risks.
Key Takeaways
- GDPR controls data acquisition, processing, and protection processes of organizations.
- Compliance with GDPR leads to trust among customers and minimizes the risk of any penalties and financial issues.
- The organization should stick to principles like transparency, data minimization, and accountability.
- Such processes as consent, data retention, breach notification, and cross-border data transfers should be handled effectively.
- The introduction of new technologies like artificial intelligence and blockchain brings up new challenges.
- Penalties and damage to the reputation can serve as a consequence of non-compliance.
- Penetration testing is essential to ensure the security of the data.
Understanding the General Data Protection Regulation (GDPR)
The EU General Data Protection Regulation (GDPR) is a data protection regulation that indicates how personal data is collected, processed, stored, and protected. The GDPR was developed by the European Union and became effective on May 25, 2018. It applies to organisations both inside and outside Europe, depending on whether their data processing falls under the scope of the GDPR.
With the GDPR, Europe is establishing its hard stance on data privacy and security at a time when more individuals are entrusting their data with cloud services, and breaches are a regular occurrence. GDPR compliance is a far-reaching proposition, especially for small and medium-sized organizations (SMEs), due to the regulation’s scale, breadth, and relative lack of specialty.
The GDPR provides extensive definitions of legal terms. The following are some of the most notable ones:
-
- Personal Data: This refers to any information about an individual who may be directly or indirectly identified. Furthermore, personal data may include location information, race, gender, biometric data, religious beliefs, online cookies, and political viewpoints.
- Data Processing: GDPR compliance requirements necessitate any action taken on data, whether automatic or human. The literature provides examples of tasks such as gathering, recording, organizing, structuring, storing, utilizing, and wiping data.
- Data Subject: The individual whose information is processed. These are your clients or website visitors.
- Data Controller: This person decides why and how personal data will be handled. Furthermore, this is for you if you are a business owner or employee who works with data.
- Data Processor: This is a third party that processes personal data on behalf of the data controller. GDPR compliance includes specific requirements for certain persons and organizations.
Are you a business looking for a GDPR service provider? Your wait has come to an end. Schedule a FREE call with our expert consultant to learn how to achieve GDPR compliance.
Why Businesses Need to Pay Attention to GDPR?
While worries about data privacy have existed for many years, many market factors are currently bringing the problem to the forefront:
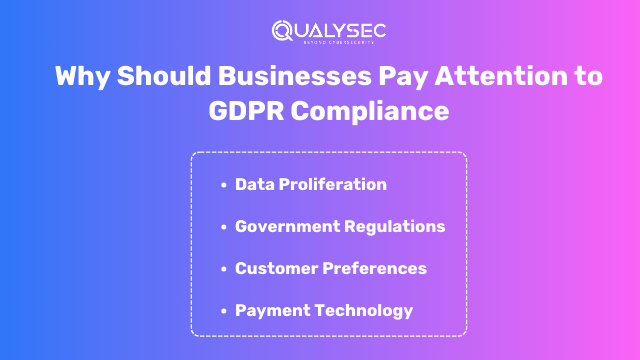
1. The Proliferation of Data
As new techniques, platforms, and applications develop, organizations have to handle an increase in data sources combined with a growth in the volume of data. Furthermore, with more consumer data scattered among providers, personal information is more likely to be exposed.
2. New Government Regulation
In addition to complying with known data privacy requirements such as GDPR and HIPAA, companies must keep up with several new regulations scheduled to be enacted in the coming months.
3. New Customer Preferences
According to recent research, 68% of consumers feel businesses profit more from data use than customers. Furthermore, customers becoming more aware of how data is gathered and utilized may be more likely to distrust firms and restrict the amount of information they are ready to contribute.
4. New Payment Technology
Customers are becoming more comfortable with various innovative payment methods, such as digital wallets, contactless payments, purchase now, pay later, and other local options. These new payment systems raise significant data privacy concerns for enterprises. And the method you use to safeguard data for one solution may differ.
Necessity of Compliance:
- Enhanced consumer trust: GDPR compliance fosters trust and credibility among customers by demonstrating a commitment to preserving their privacy rights.
- Competitive advantage: GDPR compliance can help firms differentiate from non-compliant rivals, particularly when dealing with EU clients.
- Streamlined data processes: The GDPR pushes organizations to rethink their data operations by introducing tools like data mapping, permission management, and privacy impact assessments. This can increase productivity, improve data governance, and reduce data breaches.
- Improved data security: GDPR compliance requires organizations to take strong measures to protect personal data from breaches or unauthorized access, strengthening overall data security procedures
15 GDPR Compliance Requirements for Businesses to Know About
Some essential concepts form the basis of GDPR compliance requirements, which establish rules for the right processing and management of personal data and ensure that personal data is treated lawfully and equitably. The following are the primary GDPR principles every business should know:
1. Purpose Limitation
The GDPR limits the use of data for particular activities. According to GDPR compliance, data is only “collected for specified, explicit, and legitimate purposes” under this purpose constraint.
The purposes for processing data must be explicitly defined. Furthermore, they must be explicitly stated to persons via a privacy notice. Finally, you must strictly adhere to them, restricting data processing to the objectives specified.
2. Lawfulness, Fairness, and Transparency
When processing personal data, you should have a valid basis for doing so. GDPR refers to this principle as lawfulness. Reasons for processing data may include:
-
- The user has permitted you to do so.
- You must do it to fulfill a contract.
- It is required to meet a legal responsibility.
- To preserve the vital interests of a natural person.
- It is a public work completed in the public interest.
You can demonstrate that you have a legitimate interest not outweighed by the data subject’s rights and interests.
Fairness, as defined in GDPR compliance, is synonymous with lawfulness. It means you should refrain from intentionally withholding information about what or why you collect data. Furthermore, fairness means that you will not mishandle or abuse the information you acquire.
Transparency is intimately related to fairness. Transparency is being transparent, open, and honest with data subjects about who you are, why, and how you process their data. By following it, you demonstrate fairness to your data subjects.
3. Data Minimization
Only obtain the minimum quantity of data required to fulfill your objectives. This is the GDPR’s concept of data minimization. For example, to acquire subscribers for your email newsletter, you should request the information required to distribute the emails. Avoid collecting personal information such as phone numbers or home addresses that aren’t directly relevant to your objective.
As part of your GDPR compliance checklist, review the personal data you collect and confirm that each data field is necessary for its intended purpose.
4. Accuracy
It is up to you to ensure the accuracy of the information you gather and keep. Set up checks and balances to fix, amend, or delete inaccurate or incomplete data that arrives. Schedule periodic audits to ensure the cleanliness of stored data.
5. Integrity and Confidentiality
GDPR compliance requires you to safeguard the integrity and confidentiality of the data you gather, protecting it from internal and external threats. This requires foresight and deliberate diligence. Furthermore, data must be protected from illegal processing and accidental loss, destruction, or damage.
6. Accountability
GDPR authorities understand that an entity might claim to be following all of the requirements while not doing so. That’s why they need accountability: You must have suitable methods and records in place to demonstrate your compliance with the data processing principles. Supervisory agencies might request this evidence at any moment. Documentation is essential here. It generates an audit trail you and the authorities may use to show accountability.
7. Storage Constraint
According to the GDPR, you must explain how long you store each piece of data. Setting data retention periods is an excellent way to satisfy this storage limitation requirement. In addition, set a time limit after which you will anonymize any data you are not actively utilizing.
8. Data Breach Notification
The GDPR compliance requirements explicitly define deadlines for rapid notification of data breaches. As the responsible authority, data controllers or data protection officers shall notify DPA (Data Protection Authority) in the relevant EU state of the breach as soon as they become aware and no later than 72 hours after the event. DPAs can then launch investigations and order corrective actions. In the event of a high-risk breach, data subjects should be promptly notified.
9. International Data Transfers
Any data transmission outside the European Union is considered an international data transfer and must meet specific regulations. The European Union will issue an ‘adequacy judgment’ for the nation that receives the data after assessing the robustness of its data protection laws and protections. Contractual clauses or Binding Corporate Rules (BCRs) are used in instances when adequacy determinations are not applicable.
10. Cooperation with Supervisory Authorities
Cooperation with supervisory authorities is crucial to GDPR, emphasizing the need to collaborate with data protection regulators. Organizations should be prepared to give information and help to supervisory authorities when needed. Furthermore, this cooperation includes responding to questions, accessing relevant records, and reporting to authorities about data breaches within 72 hours. Cooperation allows authorities to efficiently monitor compliance and enforce GDPR compliance requirements. Timely and honest contact with regulatory agencies is critical for demonstrating commitment to data protection and addressing difficulties.
11. Consent
According to (General Data Protection Regulation) GDPR compliance in cyber security, consent indicates that a person has been granted permission for their personal information to be collected, processed, and disclosed. Furthermore, this consent must be freely provided, specific, and informed, and the individual must have indicated their approval by clicking buttons or checking boxes. Consent regards as one of the legitimate bases and business utilize in limited circumstances.
12. Record of Processing Activities
Records of processing operations are extensive documentation kept by Data Controllers such as a GDPR compliance service provider and Processors to describe subject categories, data retention periods, security measures, and any international data transfers. Maintaining these documents is a critical component of GDPR accountability and transparency. In addition, they give a comprehensive picture of an organization’s data processing operations, allowing supervisory authorities and Data Subjects to understand how to handle Personal data.
13. Data Subject Rights Fulfillment (Articles 12–22)
GDPR gives individuals control over their personal data. Businesses must have clear procedures to handle requests to access, correct, delete, or transfer personal information and respond to objections to data processing. Most requests must be handled within one month, with limited extensions allowed under certain conditions.
14. Data Protection Impact Assessments and DPO Designation (Articles 35 & 37)
Businesses must conduct a Data Protection Impact Assessment (DPIA) before processing likely to pose high risks to individuals’ privacy, such as large-scale biometric processing or sensitive health data use. Certain organisations must also appoint a Data Protection Officer (DPO) to oversee data protection compliance.
15. Technical Security Measures While Processing Personal Data (Article 32)
GDPR Article 32 requires businesses to protect personal data with appropriate technical and organizational measures. These may include encryption, access controls, and system recovery plans. Businesses must also regularly test their security measures through vulnerability assessments and penetration testing to identify weaknesses and improve data protection.
If you want to learn about how documentation works, click below to download a sample report that can help your business achieve GDPR compliance.
Challenges in GDPR Compliance Regulations
Examine the issues that blockchain, AI, and facial recognition pose to GDPR compliance. Here are the challenges in achieving GDPR compliance:
1. AI’s Opacity
It is challenging to guarantee that AI, which has great capabilities, conforms to GDPR. GDPR requires openness, but AI can draw erroneous conclusions. It isn’t easy to understand why an intelligent computer operates the way it does.
Proposed GDPR Changes for AI in 2026
On 21 October 2026, the European Union’s Council suggested modifications to some GDPR regulations concerning AI. This is intended to make the GDPR guidelines clearer regarding the use of personal data in the creation and operation of AI technology. The goal is to support AI development while protecting people’s privacy.
2. Face Recognition and Privacy
Facial recognition technology necessitates a delicate balance between privacy and innovation since it raises concerns about consent, profiling, and the legal use of biometric data.
3. Blockchain’s Immutability
While blockchain assures data integrity, its immutability complicates GDPR’s “right to erasure” due to the difficulty of erasing data without jeopardizing the technology’s integrity.
4. Cross-border Data Transfers
Because developing technologies are global, cross-border data transfers must be carefully considered in light of GDPR’s limits on moving personal data outside the EEA.
5. Lack of legal precedents
The dynamic nature of technology creates a gap in legal frameworks, with questions about how GDPR compliance relates to specific AI algorithms, face recognition, and blockchain implementations, necessitating a balance between innovation and compliance.
What is the Cost of Non-compliance With GDPR?
GDPR non-compliance can lead to financial penalties, regulatory investigations, and reputational damage. Under the regulation, a serious breach can cause fines of up to €20 million or 4% of an organisation’s total worldwide annual turnover from the preceding financial year, whichever is higher. Other infringements may result in fines of up to €10 million.
Beyond fines, businesses may face compensation claims, loss of customer trust, and increased compliance costs. These consequences make strong data protection practices essential.
Real-World Example of GDPR Non-Compliance: The Miljödata Data Breach
In August 2025, Swedish IT company Miljödata faced a cyberattack that resulted in the theft of personal data of about 2.2 million individuals. The stolen data comprised personal identity numbers, contact details, and records relating to sick leave, rehabilitation, and student-related incidents. Some of the stolen data was later publicly available on the dark web.
The Investigation Findings:
Sweden’s data protection authority, IMY, found that Miljödata had not implemented adequate security measures to protect the personal data it processed.
- Insufficient software checks: The company failed to carry out adequate checks when installing new software, leaving it exposed to security risks.
- Lack of real-time monitoring: Its systems did not have automated, real-time monitoring to detect intrusions or suspicious activity.
What Was the Decision?
On 22 September 2026, IMY imposed a fine of SEK 1.8 million (approximately €160,000) on Miljödata for violating Article 32(1) of the EU GDPR.
What We Learned From This:
Businesses should regularly review their security controls, check software for known vulnerabilities before installation, and ensure their monitoring systems can detect suspicious activity. These measures can help reduce the risk of unauthorised access and support compliance with GDPR Article 32.
Identifying Data Security Risks Before Attackers Do: A Case Study From Qualysec
A digital event platform that supports cashless payment, ticketing, and transactions based on QR codes required better security for its web applications, mobile application, and AWS cloud platform. Penetration testing was done by Qualysec to find out any vulnerability that might endanger customer data.
What We Found
- Blind SQL injection attack: The database query may be modified to possibly reveal sensitive data.
- Broken access control: The application was vulnerable to forced browsing attacks or missing authentication checks for some functionalities.
- Insecure direct object reference (IDOR): Weak access controls allowed users to have access to ticketing or payment records of others.
- Privilege escalation attack: With weak authorization checks, users would have extra privilege beyond their own privileges.
What We Did
- Recommended parameterized database queries to prevent SQL injection.
- Addressed authentication and access control weaknesses.
- Strengthened server-side ownership checks to protect user records.
- Reviewed AWS configurations and retested affected systems after remediation.
The GDPR demands appropriate technical and organizational measures for protecting personal information. Such loopholes will make it possible for there to be unauthorized access to this data. Penetration testing will help in closing such loopholes by ensuring compliance with the GDPR requirements.
How Can Qualysec Help Organizations Achieve GDPR Compliance?
Qualysec is a CREST-accredited specialized penetration testing company that can help you discover security gaps within the systems that capture, store, and process personal data. GDPR Article 32 requires you to keep proper technical and organizational measures for data protection.
Our penetration testing helps you find exploitable weaknesses and secure your systems prior to an attacker exploiting the weakness.
We offer:
- Testing Applications and Data Environments: We assess your web applications, mobile apps, APIs, networks, and cloud environments to identify vulnerabilities that could expose personal data or allow unauthorised access.
- Identifying Real Security Weaknesses: We combine automated tools with manual penetration testing to investigate vulnerabilities, validate potential attack paths, and minimise false positives so you can focus on genuine security risks.
- Providing Actionable Security Reports: We provide detailed reports explaining your vulnerabilities, their potential impact, severity, and recommended fixes. This helps your development and security teams prioritise remediation.
- Supporting Remediation and Retesting: After you fix identified vulnerabilities, we retest the affected systems to verify whether your security fixes are effective and the original weaknesses can no longer be exploited.
- Helping You Maintain Security Records: Our penetration testing reports and retest results give you documented evidence of your security assessments. You can use these records to support internal risk reviews and demonstrate your efforts to evaluate technical security measures.
Penetration testing is one part of your broader GDPR compliance efforts. While it cannot guarantee compliance on its own, it helps you understand your security risks, address vulnerabilities, and strengthen the protection of personal data.
Conclusion
GDPR compliance requirements are not just about avoiding fines. It is about earning customer trust by protecting personal data at every stage. Understanding the GDPR compliance requirements helps businesses collect, process, store, and secure information responsibly while respecting individuals’ privacy rights. From maintaining transparent data practices to testing security controls and responding to breaches, every measure plays a role in reducing risk.
As technology and data privacy expectations continue to evolve, businesses must review their practices regularly and address security gaps before they become serious problems. Strong compliance starts with consistent action, not just written policies.
FAQ:
1. Does GDPR apply to private companies?
GDPR primarily governs data processing activities involving solely EU citizens’ and residents’ data conducted by any public or private entity globally. Furthermore, there are two exceptions to GDPR. If you gather personal data solely for personal reasons or to invite people to family activities, GDPR does not apply to you.
2. Why is GDPR important for cyber security?
The GDPR requires that organizations process personal data securely using suitable technological and organizational methods. The Regulation does not require precise cyber security measures; rather, it expects you to take ‘appropriate’ action.
3. What is the difference between GDPR and PDPA in India?
The DPDPA does not apply to personal data made publicly available by the data principals or in response to a legal necessity. No-action gaps: The DPDPA only applies to “digital personal data,” but the GDPR applies to all personal data, whether digital or not.
4. Which Business Needs GDPR COMPLIANCE?
Any firm that keeps or processes personal information on EU people within EU states must comply with the GDPR, even if it does not have a corporate presence in the EU. Companies obliged to comply must meet specific requirements, which include A presence in one of the European Union countries.