Blog
Latest Articles
Page 1 of 159 · 1425 posts
September 29, 2026
CSA Cyber Essentials Mark Certification for Singapore Businesses
Most ransomware and business email compromise cases investigated in Singapore don’t trace back to some sophisticated zero-day attack. They trace back to unsupported software still running in production, an admin account nobody remembered to lock down, or a backup that turned out not to actually restore when it mattered. The CSA Cyber Essentials Mark exists […]
September 29, 2026
EU Cyber Resilience Act Documentation: What Evidence Do Manufacturers Need?
A market surveillance authority may request the documentation required under the Cyber Resilience Act as part of its enforcement activities. Regulation (EU) 2024/2847 requires manufacturers to prepare technical documentation before placing a product with digital elements on the EU market and keep it at the disposal of market surveillance authorities. That obligation runs for at […]
September 28, 2026
Understanding ADHICS Guidelines: How to Meet the DoH Cybersecurity Standards
Your hospital may have security policies, annual vulnerability scans and an incident response plan. But can you quickly prove that every system handling health information is covered, its risks have been assessed, and the controls protecting it are actually working? This is where the ADHICS guidelines can become difficult to apply. A healthcare organisation may […]
September 28, 2026
EU Cyber Resilience Act Checklist: Requirements for Software & Digital Product Manufacturers
Most UK manufacturers tracking the EU CRA are watching one deadline. In fact, there are three, and they don’t land the same way. Compliance with the EU Cyber Resilience Act can be managed with the help of a checklist, enabling manufacturers to monitor the key stages and to plan for the compliance requirements in time. […]
September 25, 2026
Meeting RBI Cyber Security Guidelines: VAPT and Risk Standards for BFSI
I. Introduction: The Regulatory Paradigm Shift The shock of 31 July 2026 On 31 July 2026, the Reserve Bank of India repealed 628 supervisory circulars in a single stroke. The Cyber Security Framework in Banks, the 2016 circular that had anchored most Indian bank security programmes for a decade, was repealed along with the other […]
September 25, 2026
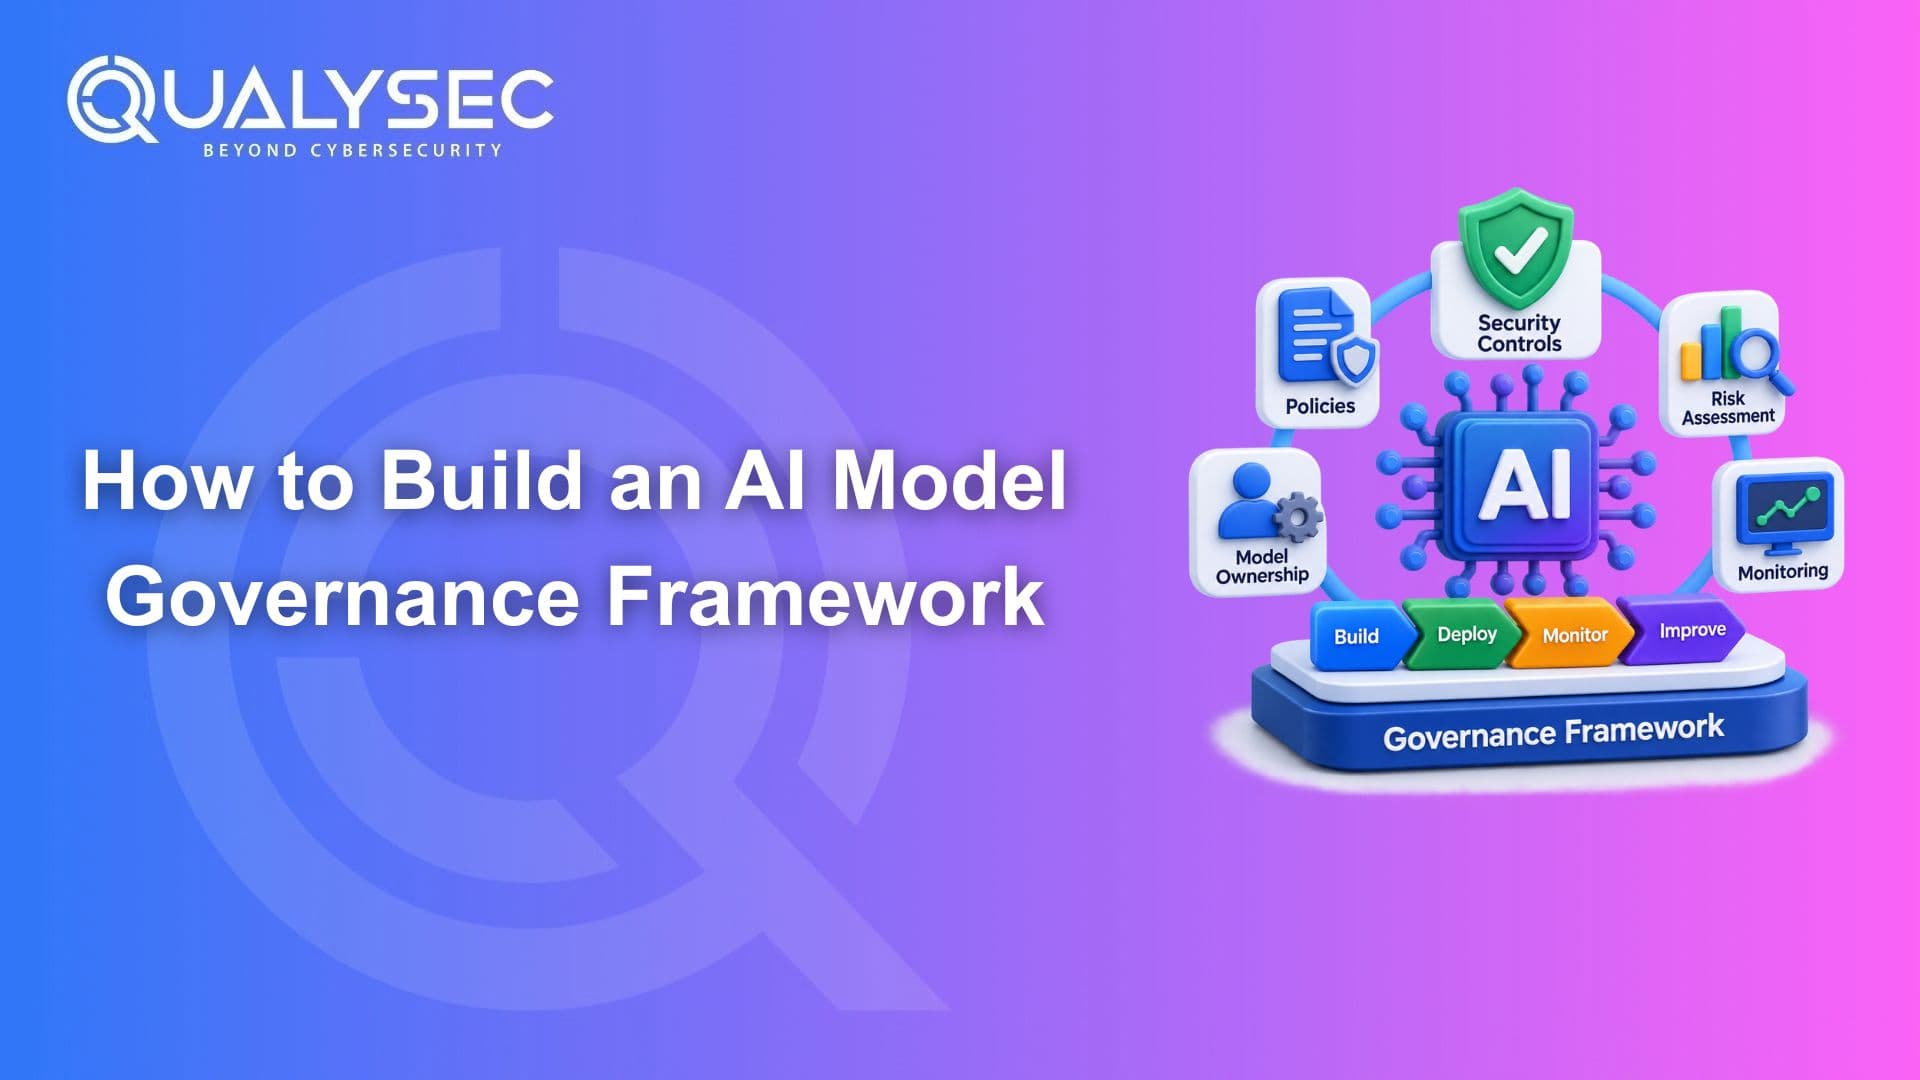
How to Build an AI Model Governance Framework
In February 2024, a Canadian tribunal ruled that Air Canada was liable for its own customer service chatbot’s invented bereavement fare policy. The airline argued the chatbot was “a separate legal entity” responsible for its own words. The tribunal rejected that argument outright. No one governed what the model could say, and Air Canada paid […]
September 25, 2026
Security Testing for Jira Extensions: A Complete Guide
Testing a Jira extension starts with understanding what the app is allowed to do inside Jira. Some extensions can read or change project data, act through granted permissions, process user information, or send data to services outside Atlassian. A security flaw in any of those paths can create risk for the Jira environment that relies […]
September 24, 2026
CREST STAR-FS: Intelligence-Led Penetration Tests (ILPT) for UK Financial Services (Beyond CBEST)
CREST STAR-FS intelligence-led penetration tests provide UK financial organisations with a structured way to assess resilience against realistic cyber attacks. Unlike vulnerability testing alone, it relies on threat intelligence and attack simulations. These assess your organisation’s ability to defend, detect, and react in case of an attack when attackers target Important Business Services. In December […]
September 24, 2026
Why Mandatory Third-Party VAPT Is Critical for DFSA Compliance
In July 2026, the UAE Cybersecurity Council said it had stopped a series of sophisticated cyberattacks targeting financial-sector organisations. The attacks tried to exploit security vulnerabilities, compromise digital systems and deploy malware. For a DFSA-regulated fintech, this raises a practical question: is a vulnerability scan enough to know whether your customer-facing systems are secure? A […]
"Don't compromise between depth and speed. Own both. Connect with Swagat, Your trusted penetration testing advisor."
Swagat Kumar Dash
Head Of Business Development