To make an app more secure, developers must make sure their apps can pass tough security tests. Luckily, some technologies can make these security tests easier and even automatic. Following best practices can also help guide and teach the testing process. This blog talks about the most common mobile app security issues and points out popular vulnerabilities. We’ll also go over recommended practices for app security testing and tools for keeping mobile apps safe in a CI/CD pipeline.
Thorough penetration testing can prevent or reduce mobile app security errors (or breaches). Hence, to keep mobile apps secure, developers and businesses are doing penetration testing. This means carefully checking the IT systems, database security, the mobile apps themselves, and any other parts that make up the app.
Following best practices for mobile app security is seen as an important part of the overall app security plan. If a company doesn’t have people with penetration testing skills for mobile apps, it is highly recommended to work with a good penetration testing company. The next paragraphs will explain the basic steps for developing an effective way to do penetration testing on mobile apps.
What is Mobile App Security?
Mobile app security keeps valuable mobile apps and your online identity safe from cyberattacks—including keyloggers, malware, tampering, reverse engineering, and other unwanted changes. A complete mobile app security plan pairs best practices and company procedures with tech solutions like mobile app shielding.
As more people everywhere use their phones for stuff like banking and shopping, keeping those apps safe has become a huge deal.
The good news is that banks are making their mobile banking security stronger for customers using mobile devices for financial services with Android and iOS application penetration testing.
Mobile app security is really important because of how much sensitive data is stored on mobile devices and how much we rely on them. Organizations and users can protect their mobile apps in advance by being aware of common mobile security threats and weaknesses.
5 Common Vulnerabilities in Mobile Apps
According to the OWASP Mobile Top 10, some of the most common app weaknesses are:
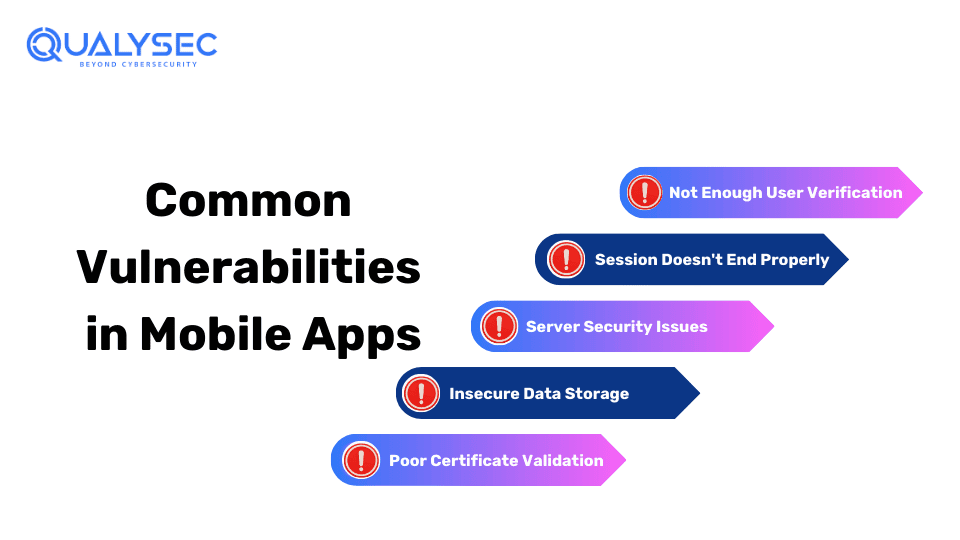
1. Not Enough User Verification
This happens when an app doesn’t properly check that the user is allowed to do an action or access data based on the security rules. User verification processes should check what a user, service, or app is permitted to do.
2. Session Doesn’t End Properly
User identifiers become invalid when a user logs out of the app. However, other users may still act on behalf of those users if the server can’t properly invalidate those identifiers. You must ensure the app has a logout button and waits until the session is correctly ended.
3. Server Security Issues
Preventing unauthorized access can be done on the server side, but input checks and limits must be built into the app to reduce load on the server. The app should verify input data during server processing and stop bad behavior.
4. Insecure Data Storage
Storing sensitive data insecurely on the device can cause vulnerabilities. Sensitive data stored on devices can potentially be stolen. Apps should store sensitive data in secure keychains. Data encryption is needed if stored on the device.
Check out Qualysec’s guide to mobile device security to see how to actually lock down your phones and protect your data.
5. Poor Certificate Validation
Mobile apps need to properly validate SSL/TLS certificates or refuse the connection if it can’t validate them. If not validated properly, data could be accessed illegally. Certificate validation must be done correctly to ensure certificates are from a trusted source.
Want to see what an actual mobile security testing report looks like? Just click the link below and download one right now!
Why Do Mobile App Security?
Mobile app security is important for developers, but it’s still not widely understood. Besides the increasing online fraud, there are various reasons why businesses should prioritize mobile app security and commit to building a complete plan.
An attack on your app could be disastrous for your company. Security testing is critical during development for the following reasons:
- Makes your app follow industry requirements.
- Gives your customers confidence in your offerings (e.g. when your app is ISO 27001 certified).
- Helps detect and understand vulnerabilities, so you can remove them and prepare for dangers like security breaches.
- Reduces the financial and reputational damage associated with cyberattacks.
- Helps you determine which parts of your app to modify: third-party code, your code, or your security personnel.
Do you need a mobile app security audit? Qualysec Technologies provides process-based VAPT services that will keep your organization secure from evolving cyber threats.
Impact on Business
| App Security Issues | Short-Term Effects | Long-Term Effects |
|---|---|---|
| Financial losses | Reputation damage | Data theft by attackers |
| Lost business | – | Man-in-the-middle attacks |
| – | – | Unauthorized communication access |
Statistics on Mobile App Hacking
-
- Over 12 million users’ login details exposed by Slack mobile app hack
- 13 Android apps leaked data of up to 100 million users
- Up to 21 million parking app users affected by hackers
- 650,000 users’ info compromised in COVID-19 passport app breach
Best Practices for Mobile App Security Testing
Before you begin, map out a clear testing plan that covers:
-
- The testing application
- Test scenarios
- Prioritizing test scenarios
- Testing approaches for mobile apps
Before checking an app for bugs, use a quick checklist so nothing slips through the cracks. It’s also smart to map out where hackers might attack early on—you can read up on mobile threat modeling to see how that works.
Use SAST, DAST, and IAST Methods:
-
- Static Application Security Testing (SAST) analyzes code without running the app to find security issues.
- Dynamic Application Security Testing (DAST) monitors the running app to detect vulnerabilities.
- Interactive Application Security Testing (IAST) combines SAST and DAST for real-time feedback. Using all three gives full coverage to identify and fix vulnerabilities.
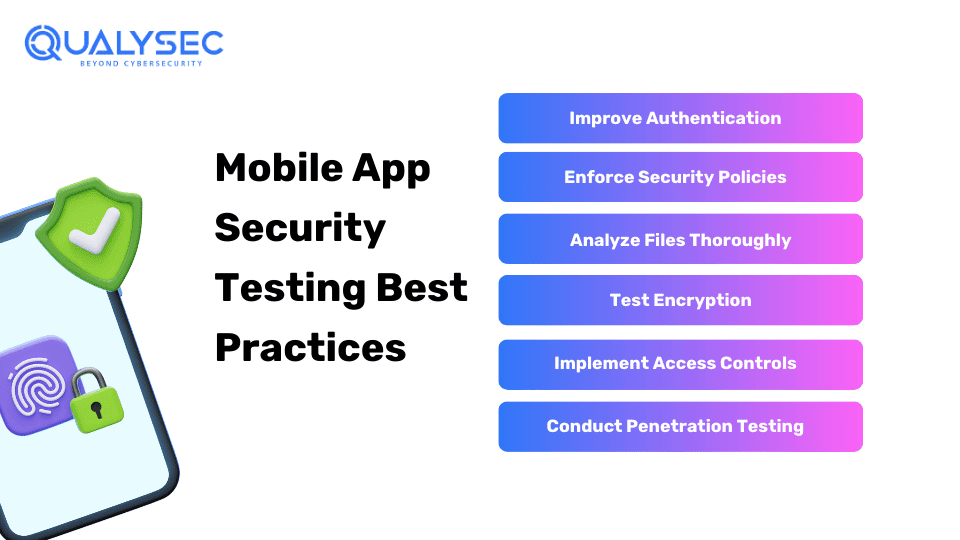
1. Improve Authentication: Implement strong user authentication like usernames, passwords, and additional verification like OTPs or biometrics. Hence, use multi-factor authentication requiring multiple credentials.
2. Enforce Security Policies: Use mobile application management to enforce policies like authentication, encryption, data protection, and access restrictions. This secures apps and devices against threats.
3. Analyze Files Thoroughly: Most apps use third-party APIs. Ensure sensitive data isn’t stored on their servers. Check for buffer overflows and SQL injection during analysis.
4. Test Encryption: Enable encryption properly across app layers containing sensitive data. Therefore, verify encryption methods using SAST tools.
5. Implement Access Controls: Limit what users can view/do in your app using access controls like role-based access control (RBAC).
6. Conduct Penetration Testing: Conducting regular penetration testing is important. The firm should hire ethical hackers who try to break into the systems and networks, just like real attackers would. This proactively identifies vulnerabilities before they can be exploited, and conducting this regularly helps improve security measures.
Conclusion
Mobile app security is crucial these days as it ensures the application is secure from the end-user’s perspective, especially when evaluating Android vs iOS protection standards. In this blog, we covered the best practices for strong iOS and Android app security.
If you are evaluating top mobile app security companies, many mobile app developers and businesses choose to work with a trusted partner like Qualysec, a leader in providing process-based mobile application penetration testing services. Instead of building an in-house team from scratch, we recommend bringing on an experienced partner to execute a mobile app pen testing plan more quickly. Therefore, feel free to contact us now!
FAQ’s
Q: What are the common security threats in mobile applications?
A: The Common threats to mobile applications are as follows:
-
- Lack of encryption
- Insecure data storage
- Insecure authentication
- Weak credentials
Q: What are mobile application testing types?
A: The three categories of mobile app testing:
-
- Black box
- White box
- Gray box testing.
Q: What is penetration testing in mobile applications?
A: Mobile App Penetration Testing is the process of testing mobile apps to find and expose any weaknesses or vulnerabilities. Hence, before hackers can exploit them, assess the level of threat they pose to the app by testing them manually or automatically using tools.


