FFIEC compliance has emerged as a vital pillar for financial institutions in the United States. Additionally, banks, credit unions, and other federal financial supervisors should be familiar with FFIEC compliance. Nowadays, the world of the Internet is changing quickly and, therefore, security requirements imposed by regulatory authorities are stringent. Thus, FFIEC compliance offers a multifaceted framework that assists financial organizations in securing sensitive information and sustaining the resilience of their operations. Moreover, compliance with these standards not only provides regulatory alignment but also develops customer trust. This paper will examine the meaning of FFIEC compliance, its major requirements and how institutions can be able to apply these guidelines.
What is FFIEC and Why Does Compliance Matter?
The Federal Financial Institutions Examination Council (FFIEC) was formed in 1979 as a five-member interagency organization of the U.S. Government. Moreover, its main mission entails prescribing uniform principles, standards, and report forms to be used by the federal financial institutions. This body is made up of the five banking regulators, namely the Board of Governors of the Federal Reserve System (FRB), the Federal Deposit Insurance Corporation (FDIC), the National Credit Union Administration (NCUA), the Office of the Comptroller of the Currency (OCC), and the Consumer Financial Protection Bureau (CFPB).
The compliance of the FFIEC stipulates that financial institutions comply with the standards of online banking technologies. Notably, these standards were first released in October 2005 and have since changed greatly. Companies that comply with the FFIEC requirements are obliged to have a consistent, holistic audit of their internal environment. The main objective of these reviews is to identify the potential weaknesses of security and any threats.
Who Needs to Follow FFIEC Guidelines?
Several financial institutions have to comply with FFIEC:
- Member banks in the Federal Reserve System are state-chartered banks.
- Thrift holding companies and bank holding companies.
- Foreign banking organizations that have branch agencies, commercial lending subsidiaries or bank subsidiaries located in the United States.
- Subsidiaries, which are non-financial, of federally monitored financial institutions.
Moreover, non-compliance with FFIEC compliance may lead to huge financial fines. Even though the FFIEC provides recommendations, its member agencies have the power to impose fines. As a result, up to 2 million may be paid by the institutions as financial penalties. Furthermore, the breach of banking regulations by organizations may result in litigation in the federal court system.
Don’t risk penalties — Book your FFIEC risk gap assessment with Qualysec experts today to stay compliant.
What Are the Core Components of FFIEC Cybersecurity Guidelines?
The FFIEC cybersecurity guidelines have several areas that are very critical and need to be addressed by financial institutions. Thus, one must be familiar with these elements in order to accomplish full FFIEC compliance.
The FFIEC IT Handbook and Booklets
The FFIEC IT Handbook InfoBase is a rich source of materials in the form of work programs or IT booklets. It also contains data on legislation, regulations, and advice. The InfoBase comprises 11 booklets that touch on issues of audit and business continuity planning in outsourced technology services. Specifically, these booklets address:
- Audit: The booklet helps organizations to adopt effective IT audit functions. It includes IT audit positions, independence, staffing, and risk-based auditing strategies.
- Business Continuity Planning: This section helps financial establishments to be able to provide important operational services. In addition, it also covers business impact analysis, risk assessment, and risk management strategies.
- Information Security: This is a broad-based booklet that explains what financial institutions must do when they develop their Information Security Program. Moreover, it contains the elements of governance, such as establishing a security culture and distributing responsibility.
- Operations: It provides guidelines on the operational information security risks that the financial institution’s cybersecurity standards should address. As a result, it is target-oriented at the proactive process of threat management.
FFIEC Cybersecurity Assessment Tool
In June of 2015, the FFIEC issued the Cybersecurity Assessment Tool, helping financial institutions to get a maturity assessment of information security. Notably, through this tool, inherent risk profiles are measured in five categories:
Types of connection and technologies:
- Technologies and connection types
- Delivery channels
- Online/Mobile products and technology services
- Organizational characteristics
- External threats
Additionally, the assessment tool evaluates Cybersecurity Maturity Levels across five primary domains:
- Cyber risk management and oversight
- Threat intelligence and collaboration
- Cybersecurity controls
- External dependency management
- Cyber incident management and resilience
Consequently, through the assessment of the inherent risk, as well as the level of maturity, organizations will be able to identify whether their security measures are adequate. Thereafter, in case of imbalances, corrective actions may be taken by the enterprises.
To understand how structured cybersecurity frameworks work, read Penetration Testing Framework: Steps, Tools, and Best Practices
How Do Financial Institutions Conduct FFIEC Risk Assessment?
It will take a systematic approach to conduct an efficient FFIEC risk assessment. Furthermore, the organizations are expected to adhere to the set procedures that entail extensive assessment. Thus, the gap assessment methodology will be presented in the following steps:
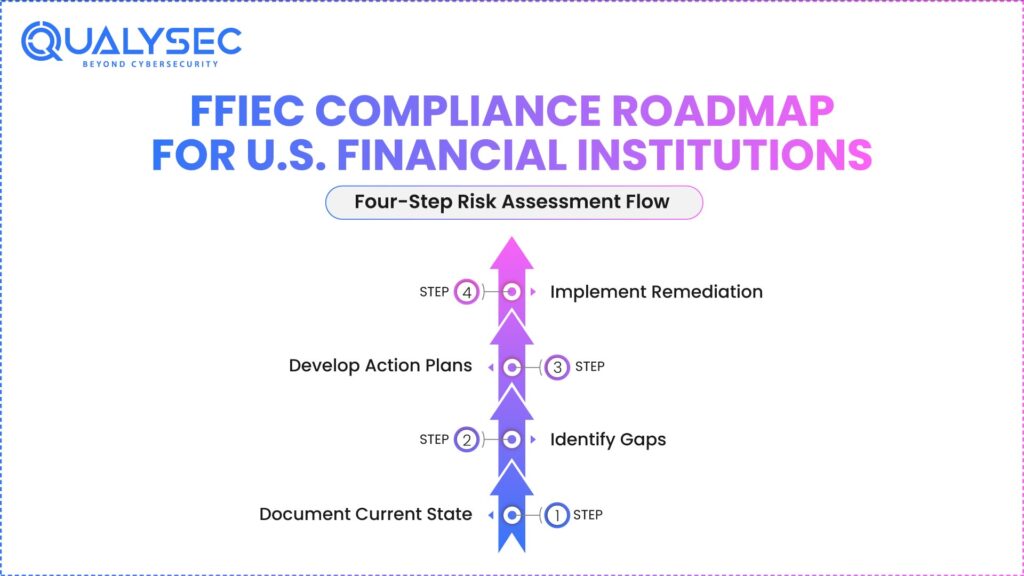
Step 1: Document Current State
The initial step is the recording of the current cybersecurity posture of the financial institution. Organizations are able to use the FFIEC Cybersecurity Assessment Tool and other info bases. Moreover, they are able to develop templates of controls and processes, which are outlined in the FFIEC compliance requirements, using these resources.
Step 2: Identify Gaps
Then, the institutions perform an analysis of their present cybersecurity level. As a result, the comparison of the organizational processes to the required FFIEC cybersecurity guidelines prevents any gaps in compliance. Notably, the third-party vendors offering services to the institution should be included in the assessment.
Step 3: Develop Action Plans
After gap analysis, the organization develops action plans in order to rectify the observed problems. Besides, businesses should pursue systematic steps to mitigate cybersecurity process failures. Thus, the use of such frameworks as NIST can be used to develop the required organization of this stage.
Step 4: Implement Remediation
Lastly, the institutions put action plans into practice, developed in earlier stages. The management will have to be at the forefront in spearheading these efforts. Moreover, the continuous assessment of cybersecurity is the procedure that guarantees continued improvement. As a result, a cybersecurity culture ensures that organizations and customers are not compromised.
Talk with Qualysec experts to get your FFIEC risk and cybersecurity posture assessed today.
What Are FFIEC Penetration Testing Guidelines and Requirements?
The FFIEC penetration testing guidelines form a significant part of an overall evaluation of security. Moreover, the guidelines allow financial institutions to recognize their vulnerabilities in advance before they are exploited by malicious actors.
Understanding Penetration Testing Under FFIEC
Although the FFIEC penetration testing guidelines do not specifically require penetration testing as an independent requirement, they place heavy emphasis on the frequency of security testing. Besides, the Information Security booklet addresses the need for independent security testing. Thus, a significant number of financial institutions include penetration testing as the usual element of their overall security programs.
FFIEC compliance requirements specify that organizations must:
- Conduct regular vulnerability assessments
- Perform independent security reviews
- Test incident response procedures
- Evaluate third-party vendor security
Moreover, the institutions can test the security controls effectively by means of penetration testing services. The weaknesses of systems, applications, and network infrastructure are therefore known through these tests.
Learn more about why ongoing testing matters — Automated Compliance Tools Vs Penetration Testing
Key Testing Areas
Financial institution cybersecurity standards require testing across multiple domains:
| Testing Domain | Purpose | Frequency |
| Network Infrastructure | Identify network vulnerabilities and misconfigurations | Quarterly |
| Web Applications | Test for OWASP Top 10 vulnerabilities | Annually |
| Social Engineering | Assess employee security awareness | Semi-annually |
| Wireless Networks | Evaluate wireless security controls | Quarterly |
| Physical Security | Test physical access controls | Annually |
| Cloud Environments | Assess cloud configuration and security | Quarterly |