
Blog
Latest Articles
Page 14 of 158 · 1421 posts
July 22, 2026
What Is ADHICS Compliance? Complete Guide, Checklist & Benefits
In the UAE, cyberattacks on healthcare facilities surged 37% in 2024, with ransomware incidents rising 45% amid the expansion of digital health adoption. DoH specifically requires all licensed clinics, hospitals, and other health centres to adhere to ADHICS Compliance to ensure that patient information remains confidential, correct, and accessible. The ADHICS standard also aligns with […]
July 22, 2026
BSP Cybersecurity Framework Explained: Compliance Guide for Philippine Banks and Fintechs
BSP cybersecurity framework refers to the set of “technical controls” developed and promoted by the Bangko Sentral ng Pilipinas (BSP) to protect the Philippine financial system. The rise of digital banking, e-money, and open finance laid the foundation for widespread digital financial adoption in the Philippines. In recent years, the Bangko Sentral ng Pilipinas (BSP) […]
July 21, 2026
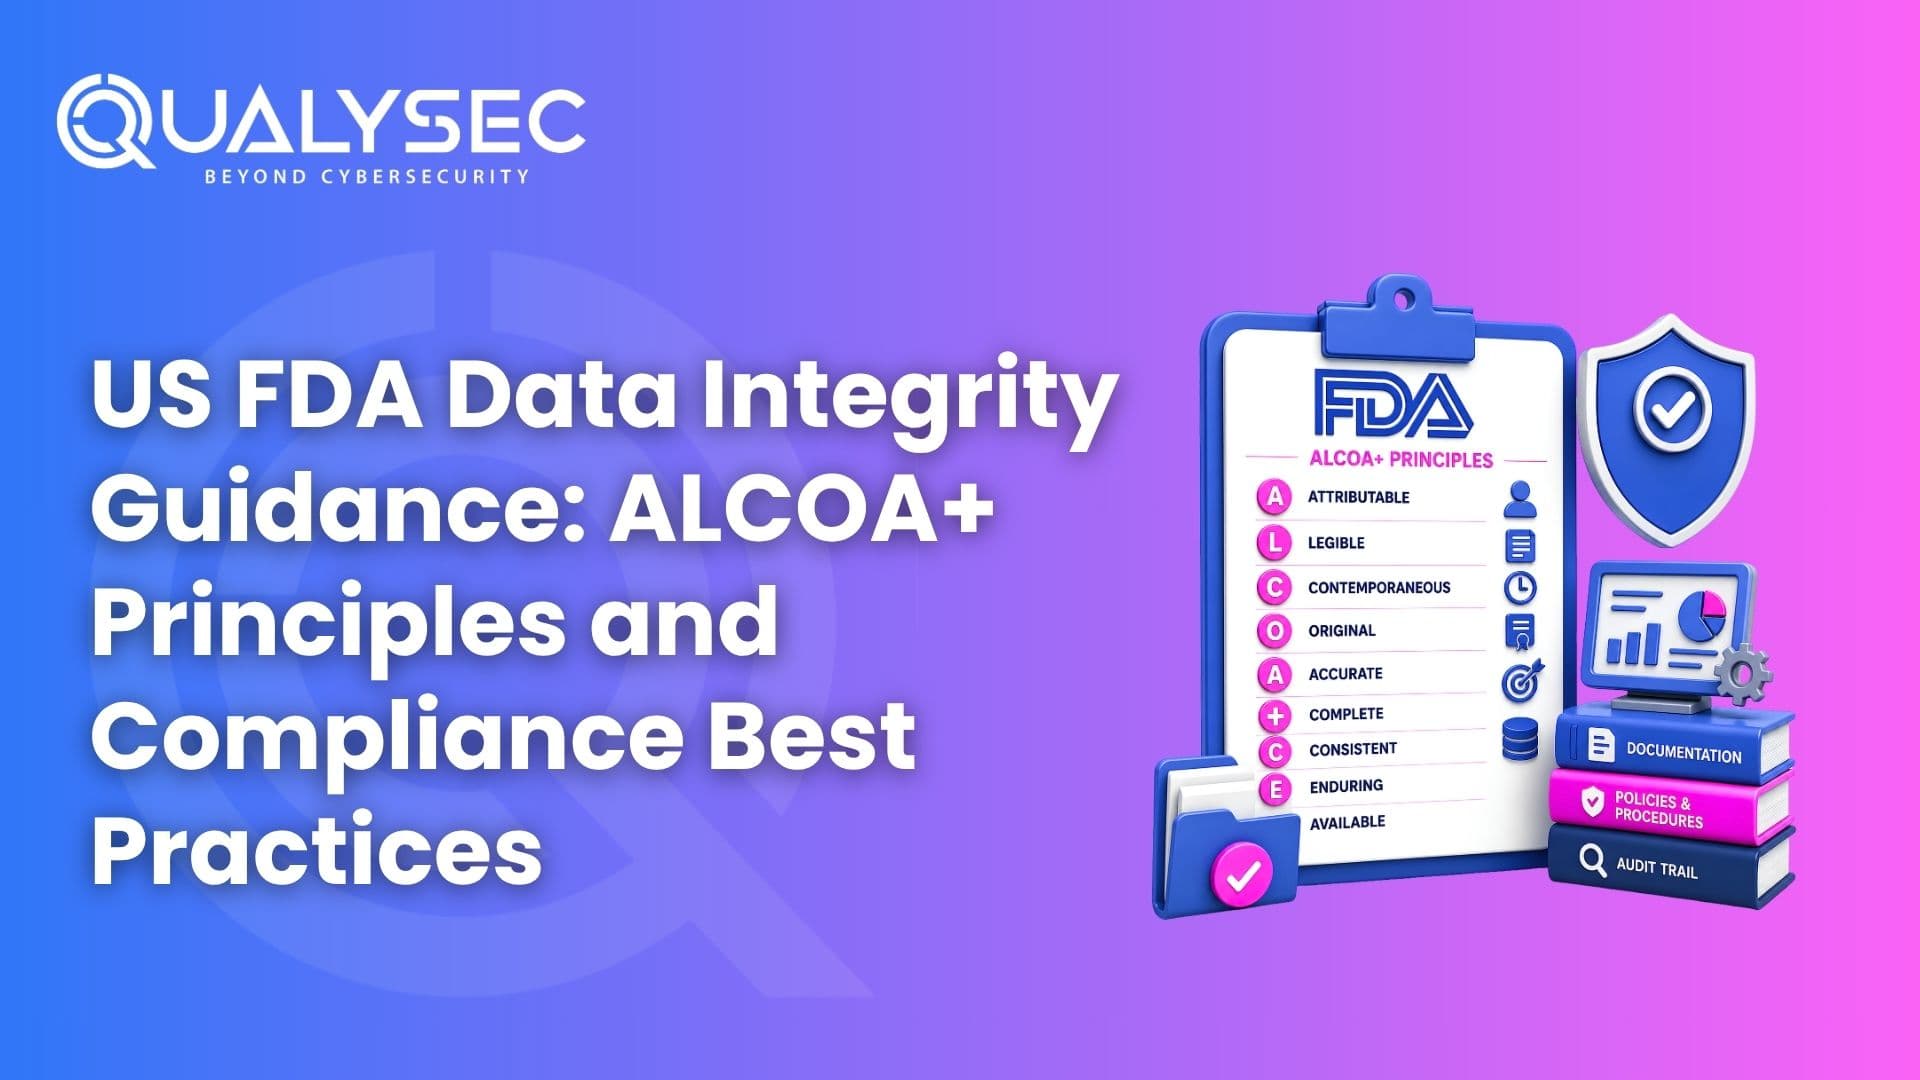
US FDA Data Integrity Guidance: ALCOA+ Principles and Compliance Best Practices
A shared login may seem harmless until an FDA investigator asks who changed a result. A missing chromatographic file, an unexplained reintegration, or an altered worksheet can cast doubt on far more than one test. It may undermine the evidence used to approve or reject an entire batch, as emphasized in the US FDA Data […]
July 21, 2026
M&A Security: A Complete Cybersecurity Due Diligence Guide
M&A security is a discipline that involves the assessment and management of the cyber risk of the target company prior to, during, and after an acquisition. When you purchase a company, you are buying in its flaws, its liabilities, and its adversaries. Strong M&A security can help identify those risks, and you would not have […]
July 21, 2026
Top 10 DPDP Consultants in India (2026): Best Compliance Experts
The Digital Personal Data Protection Rules 2025, notified by the Ministry of Electronics and Information Technology on November 13, 2025, set the maximum penalty for failing to implement reasonable security safeguards at ₹250 crore per violation under Schedule 1 of the Act. That single number has pushed DPDP consultants from a legal team’s to-do list […]

July 20, 2026
Red Team Services: Strengthen Your Cyber Defenses
Do you believe that your organisation will be able to counteract advanced cyber threats? Red team services are the final test of your security posture because it is simulated in the real world. Additionally, these sophisticated tests extend far beyond standard security tests. Thus, they provide organisations with an overall analysis of their detection and […]
July 18, 2026
Kubernetes Penetration Testing: Complete Methodology, Tools, Vulnerabilities & Best Practices
This guide covers everything about what Kubernetes Penetration Testing is, why it is important, and why Kubernetes clusters need regular penetration testing, penetration methodology, and tools. Most cloud-native apps now run on the backbone of Kubernetes, and the popularity has made it the favorite target for attackers. Red Hat’s State of Kubernetes Security report found […]
July 17, 2026
A Guide to CREST Penetration Testing: Process, Benefits and Provider Selection
An enterprise prospect asks whether your latest penetration test was performed by a CREST-accredited provider. Your team has a recent penetration test report, but suddenly that isn’t enough. Should you repeat the assessment, or is CREST simply another certification logo? Before choosing a CREST penetration testing provider, it helps to understand what a CREST engagement […]
July 17, 2026
Consequences of Non-Compliance: Risks, Penalties, and How to Stay Protected
Key Takeaways Noncompliance costs 2.71 more. The cost of maintaining a compliance program is $5.47 million per year, whereas the cost of doing nothing increases to $14.82 million per year. While penalties for non-compliance are heavy, downtime followed by reputational loss is the most common type of loss. New regulations (like NIS2, DORA, and HIPAA) […]
"Don't compromise between depth and speed. Own both. Connect with Swagat, Your trusted penetration testing advisor."

Swagat Kumar Dash
Head Of Business Development