Blog
Latest Articles
Page 1 of 155 · 1394 posts
September 15, 2026
CREST Accredited Penetration Testing for HKMA iCAST (Hong Kong)
Identification of vulnerabilities is just one step in assessing the bank’s cyber resilience. Financial organizations must know if attackers can take advantage of the vulnerabilities identified in order to gain access to important banking systems. This is where penetration testing companies with CREST-accreditation become relevant, particularly for institutions preparing for HKMA’s intelligence-led testing requirements. The […]
September 15, 2026
Understanding the New CREST AI Security Testing Accreditation
The integration of AI into cybersecurity activities and enterprises is growing quickly. This is why CREST has officially launched AI Security Testing Accreditation. Through this accreditation, CREST evaluates a provider’s technical expertise, testing methodologies, governance, and controls for conducting AI security assessments. Currently, 69% of penetration testing providers use automated machine learning applications, and 76% […]

September 11, 2026
NIST Cybersecurity Framework 2.0: Everything CISOs and Tech Leads Need to Know
Two years after publication, the NIST Cybersecurity Framework 2.0 has become the document most boards ask about by name. It is the most downloaded NIST technical publication, with over 3 million views and downloads, and it is no longer a US critical infrastructure document. It is a global reference used by banks in São Paulo, […]

September 11, 2026
NIST Secure Software Development Framework (SSDF): The Complete Technical & Compliance Guide
One weak software dependency can disrupt hospital operations and compromise patient information within a day. Developing healthcare software in an insecure manner results in late-stage patches, audit failures, and delayed product release. This is why the NIST Secure Software Development Framework (SSDF) is essential for the healthtech community. Integrating the NIST 800- 218 practices allows […]

September 11, 2026
External Attack Surface Management (EASM): Why Continuous Defense Beats Point-in-Time Assessments
Your external attack surface does not stop changing when a penetration test ends. A new cloud instance can go live, a forgotten subdomain can remain exposed, or a previously safe service can become vulnerable after a configuration change. IBM’s 2026 Cost of a Data Breach Report puts the global average cost of a data breach […]
September 10, 2026
How to Fulfill the Security Requirements of a GDPR Data Protection Impact Assessment (DPIA)
Introduction In late 2025, Spain’s data protection authority fined AENA just over €10 million in connection with its use of biometric facial-recognition systems at airports. The case raised concerns around the organisation’s data protection impact assessment (DPIA), including how it assessed the necessity, proportionality and risks of the processing. The authority also imposed corrective measures […]
September 10, 2026
What is Application Security Posture Management (ASPM)? Definition, Architecture and Best Practices
Application security posture management (ASPM) is a control layer that ingests findings from every security tool you already run, removes the duplicates, adds context about what each finding can actually reach, and turns the result into a ranked list somebody can work through. Gartner defines the category as tools that continuously manage application risk through […]
September 10, 2026
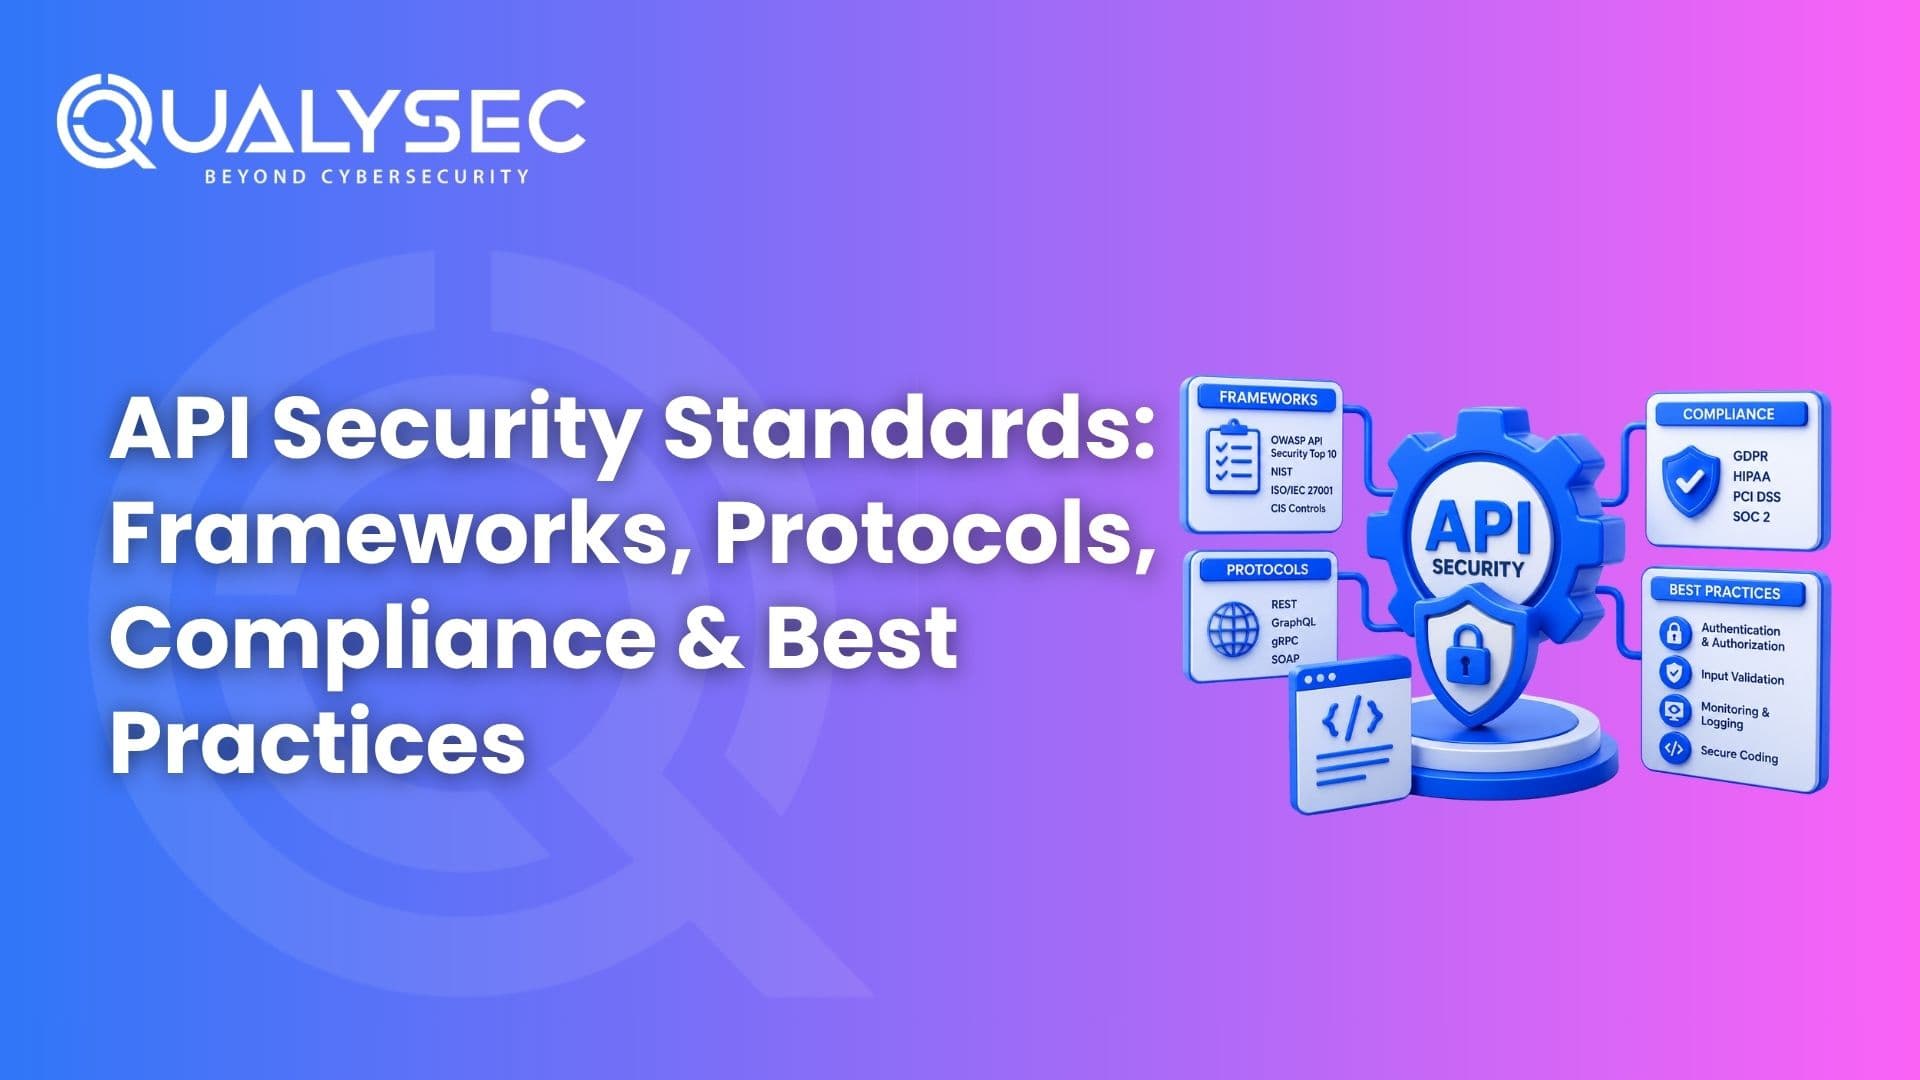
API Security Standards: Frameworks, Protocols, Compliance and Best Practices
What Are API Security Standards? API security standards are published and verifiable rules that outline how the API must prove its authentication, authorisation, data protection and everything else in transit to an auditor. They are from various sources: standards bodies such as OWASP and NIST, protocol specifications such as OAuth 2.0 and OpenID Connect, and […]
September 10, 2026
APRA CPS 234 Penetration Testing: How to Meet the Information Security Testing Mandate
APRA CPS 234 is the information security standard APRA regulated organisations in Australia use to guide how they manage cyber risk and protect critical information assets. The harder part is turning that expectation into a testing program that reflects the actual risk around your information assets. Penetration testing can play an important role here by […]
"Don't compromise between depth and speed. Own both. Connect with Swagat, Your trusted penetration testing advisor."
Swagat Kumar Dash
Head Of Business Development