Qualysec

Webinars

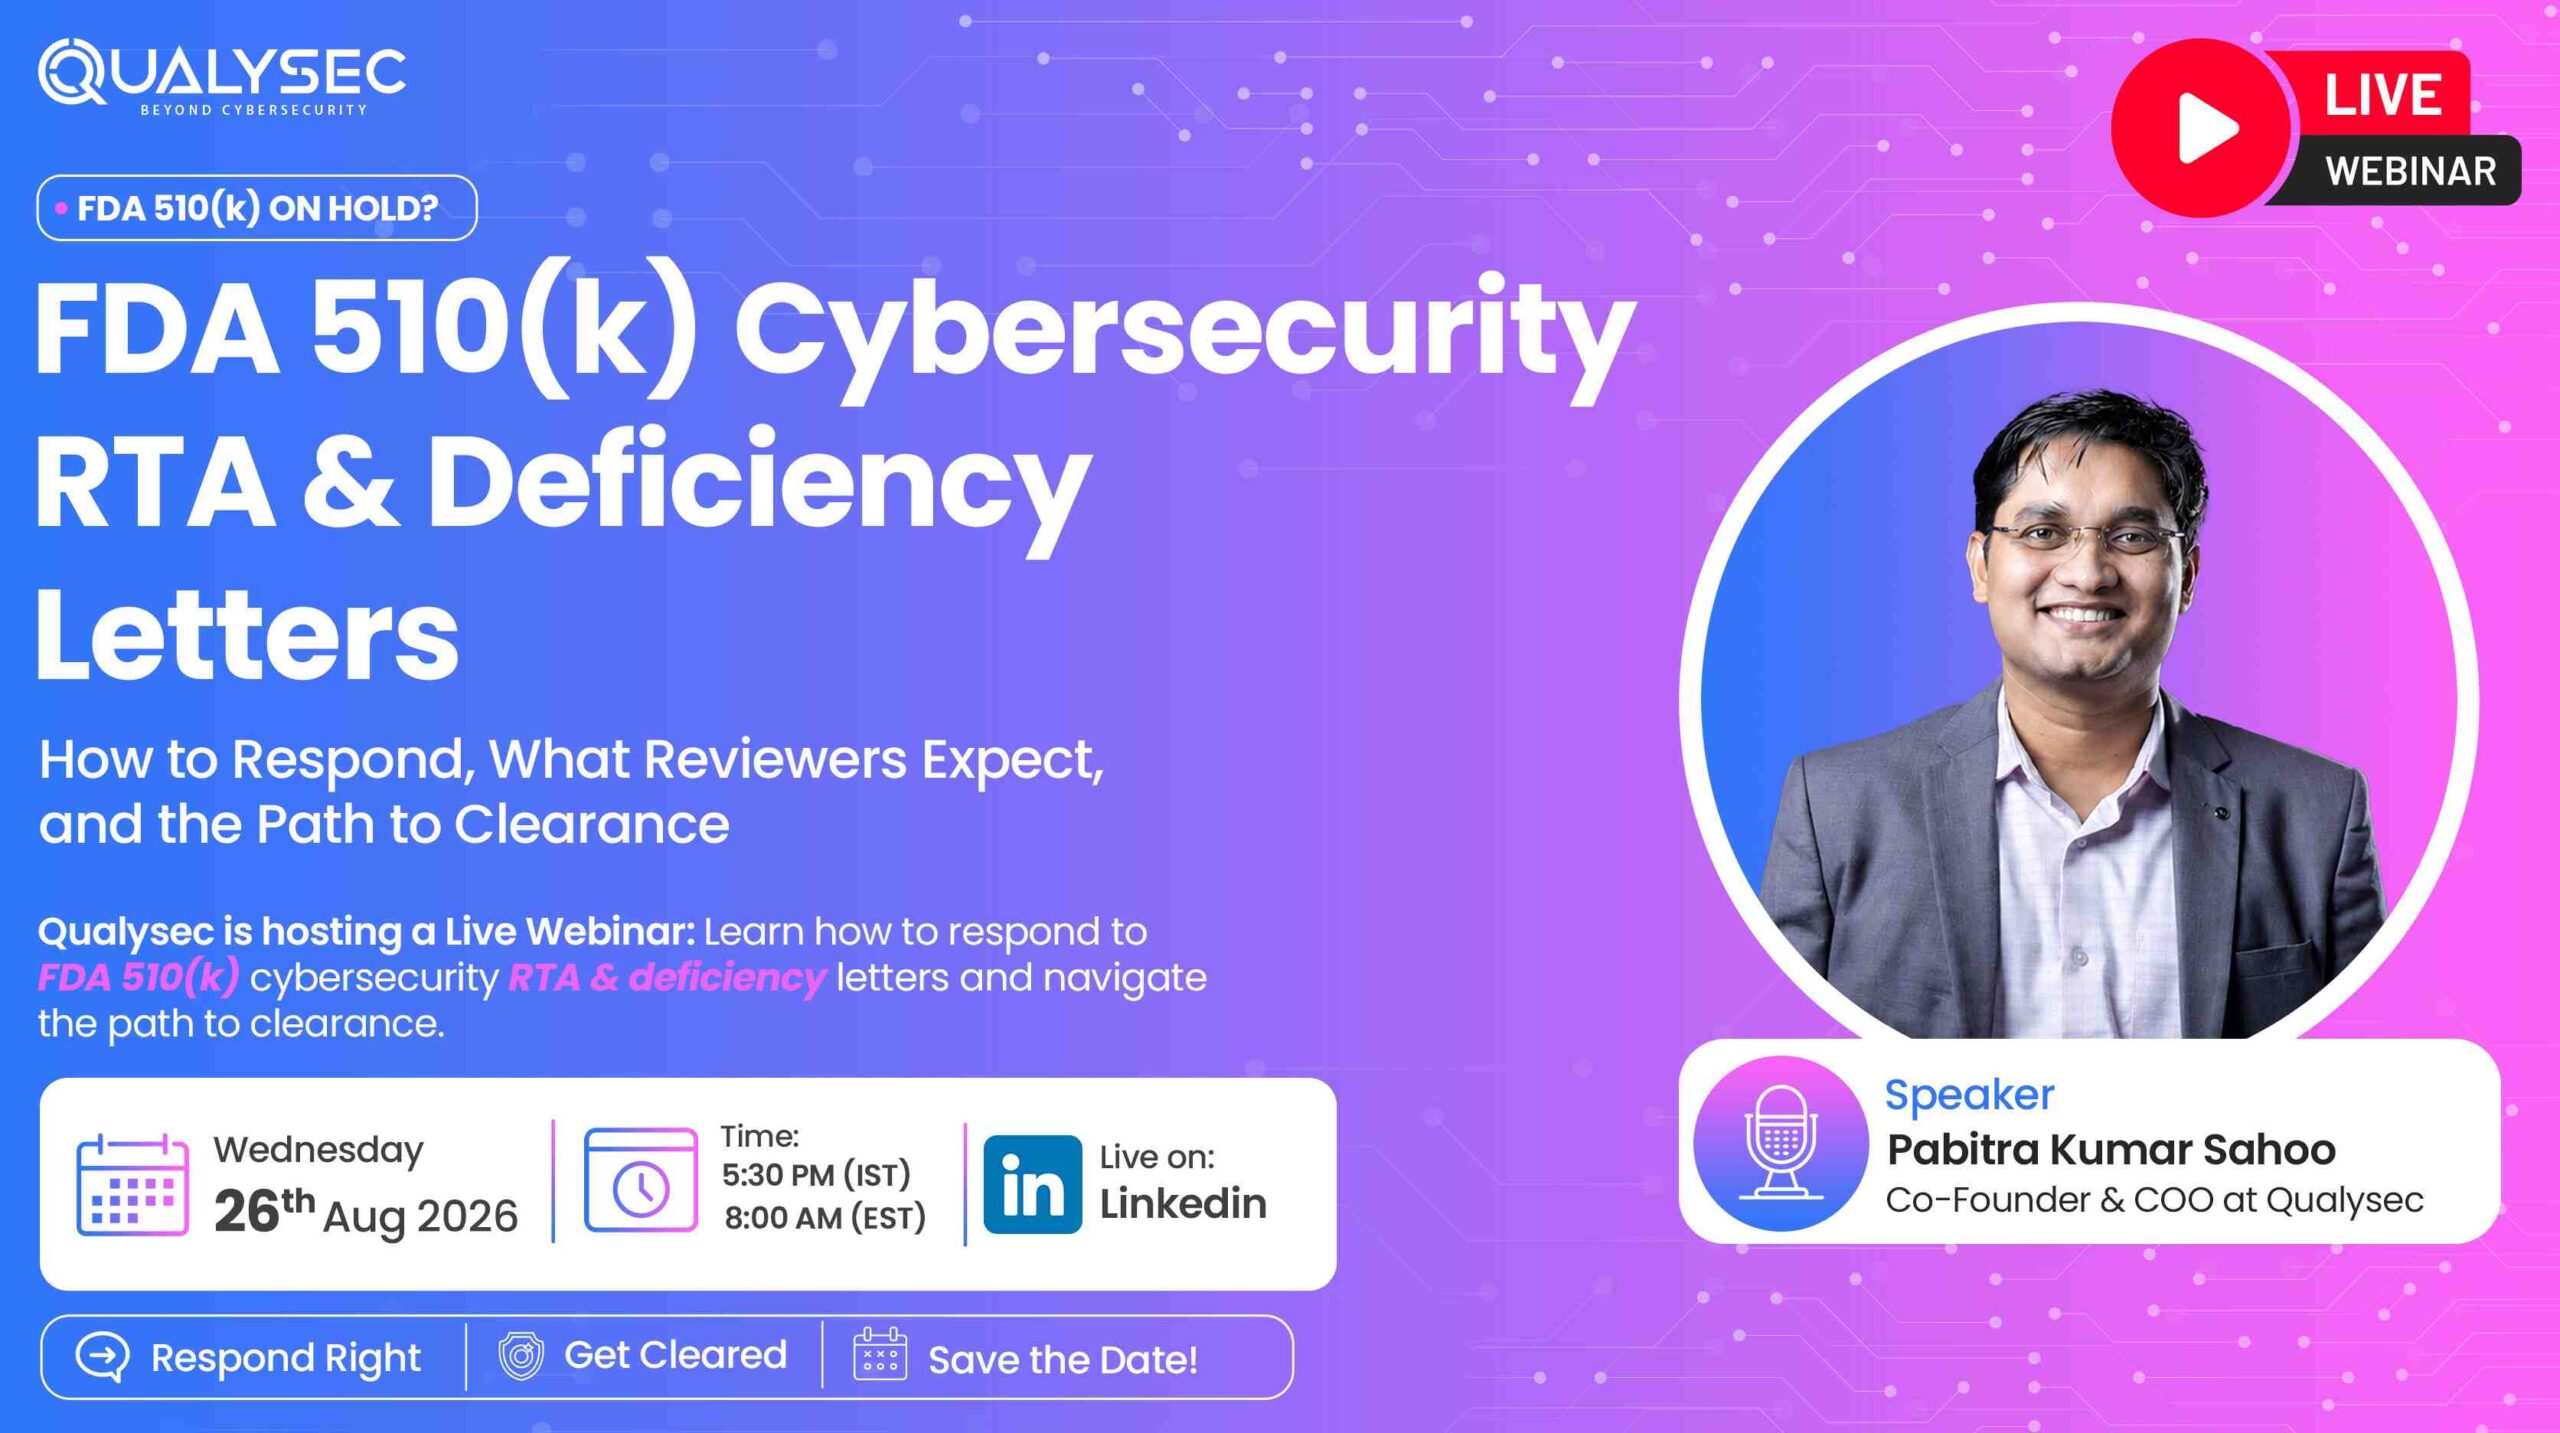
Building an FDA 510(k) Threat Model Report: What Reviewers Expect in 2026 and Beyond

Wed, October 28, 2026
05.30 PM

Event Details

  • Date: Wed, October 28, 2026
  • Time: 05.30 PM
  • Platform: LinkedIn Live
  • Live Streaming: LinkedIn

One of the most important medical device cybersecurity documentation reports is a threat model report. In the case of FDA 510(k) submissions, it should detail the device’s system architecture, potential attack surfaces, identified cybersecurity threats and associated risks, and measures taken to address these risks.

But threat identification has only started with one part. Medical device manufacturers also must be able to show how and when threats are assessed, how cybersecurity risk is used to inform choices for mitigation, and how the security controls are backed by the appropriate evidence of verification and validation.

In this webinar, Qualysec Technology explores the key elements of an FDA 510(k) threat model report and the documentation considerations that matter during premarket review. Learn how to represent system architecture, identify potential attack scenarios, apply structured threat modeling methodologies, and establish traceability between threats, risks, controls, and testing evidence.

In this session, your regulatory and engineering teams will gain insights into what documentation is missing and how to create a more comprehensive threat model report for their FDA 510(k) submission or review.

What You Will Learn

In this session, you’ll gain practical advice on organizing the documentation of medical device threat modeling and how to link medical device cybersecurity analysis with evidence to support FDA premarket submissions.

You will learn:

  • Understanding FDA 510(k) Cybersecurity Expectations: Dive into the concept of threat modeling in cybersecurity premarket documentation, and the considerations under Section 524B of the FD&C Act for applicable cyber devices.
  • Defining the Medical Device System: Understand how architecture diagrams, data flows, interfaces, trust boundaries and system components define the scope of a threat model.
  • Identifying Attack Surfaces and Threat Scenarios: Identify potential threats related to wireless, cloud, 3rd party software, external interfaces and connected systems.
  • Applying Threat Modeling Methodologies: Understand how methodologies like STRIDE and attack trees can be used to understand potential attack paths and assess the threat that could be posed by a cyber attack.
  • Connecting Threats With Cybersecurity Risks: Relate the elements of threat scenarios to threat risk assessment, risk mitigation and choice of appropriate security controls.
  • Establishing Traceability and Supporting Evidence: Discuss ways of linking identified threats to risk assessments, security controls, and penetration testing or other supporting evidence.
  • Recognising Common Threat Model Documentation Gaps: Identify gaps in the documentation of the threat model, including missing architecture views, unclear trust boundaries, unsupported model assumptions, and missing links between threats and implemented controls.

This webinar focuses on practical threat modeling and documentation considerations informed by FDA premarket cybersecurity guidance.

Who Should Attend

This webinar is designed for Regulatory Affairs (RA) professionals, Quality Assurance (QA) leads, medical device cybersecurity engineers, product security leaders, medical device founders, Chief Technology Officers (CTOs), software development teams, and submission owners involved in preparing or reviewing FDA 510(k) cybersecurity documentation.
Quick Submission Readiness Check (optional)

  • Confirm whether your medical device falls within the applicable Section 524B cyber device criteria.
  • Check whether the threat model reflects the device architecture, trust boundaries, data flows, external interfaces, and relevant dependencies.
  • Verify that identified threats are connected to cybersecurity risk assessments and appropriate mitigation measures.
  • Ensure that security controls and risk mitigation claims are supported by relevant verification, validation, and testing evidence.
  • Review whether the threat model, security architecture, SBOM, and other cybersecurity documents present a consistent and traceable account of the device’s security.
Building an FDA 510(k) Threat Model Report What Reviewers Expect in 2026 and Beyond

Subscribe to Newsletter

Previous Webinars

top-left-coin
left-coin
top-right-coin
calculator

PRICING

How Much Does A Penetration Testing Cost?

Get a Quote

Want To Protect Your Organization from Emerging Cyber Threats?

Now is the perfect time to stay one step ahead of evolving cyber threats by taking proactive security measures. Fill out the form, and our expert pentesters will help you identify and address vulnerabilities before they escalate.

Total No. Of Vulnerabilities

0+

Total No. Of Vulnerabilities

Years in Business

0+

Years in Business

Assessment Completed

0+

Assessment Completed

Trusted Clients

0+

Trusted Clients

Countries Served

0+

Countries Served