
Blog
Latest Articles
Page 5 of 158 · 1418 posts
September 8, 2026
MHRA Cybersecurity Guidelines: Why Medical Device Penetration Testing Is Non-Negotiable
Medical devices now rely on much more than the device itself. Many depend on software, cloud services, mobile apps, APIs, or hospital networks to work as intended. That creates a simple problem for manufacturers. A security flaw may not stop at data exposure. If someone can interfere with software, communications, or device settings, the effect […]
September 7, 2026
HITRUST Documentation Requirements: Essential Evidence for CSF Certification
HITRUST assessments can be challenging if the proof of adequate security measures is spread among many individuals, systems, and software. HITRUST documentation collects all this information together, including policy statements, access audits, and security vulnerability assessments. If documentation is not complete or is gathered last minute, then you will waste time tracking down the records. […]
September 5, 2026
The Complete SEBI CSCRF Compliance & VAPT Guide: Requirements, Deadlines, Checklist & Choosing a CERT-In Auditor
If you run a broker, an AMC, a depository, or any SEBI-regulated business, SEBI CSCRF Compliance is no longer a project with an end date. The deadlines have passed, and the framework is fully in force. Examiners now ask a sharper question: not whether you are ready, but what your evidence shows. This guide walks […]
September 5, 2026
Recent Cyber Attacks in India 2026: Major Breaches, Emerging Threats & How to Stay Protected
India entered 2026 with cyber risk already operating at an enormous scale. In 2025 alone, CERT-In handled 29,44,248 cyber security incidents. That figure covers incidents reported to and tracked by the agency, so it should not be read as 29.44 lakh confirmed data breaches. What makes Cyber Attacks in India worth watching now is not […]
September 4, 2026
How to Achieve ISO 42001 Certification for AI Governance
AI adoption inside enterprises has moved faster than most governance functions can keep up with, and regulators have stopped waiting for that gap to close on its own. Under the EU AI Act, prohibited practices have carried fines of up to €35 million or 7% of global annual turnover since February 2025, with enforcement powers […]
September 4, 2026
Navigating HITRUST v11 Requirements: What Has Changed for Healthcare Orgs
Recently, we have observed that Healthcare organizations are facing various kinds of cybersecurity issues while protecting their patient data. They also have to secure their systems while keeping the clinical systems, cloud infrastructure, API, and various digital applications operational. The implementation of HITRUST v11 will redefine cybersecurity assurance in healthcare organizations. Organizations can secure sensitive […]
September 3, 2026
How Much Does HITRUST Compliance Cost in 2026? Complete Pricing & Savings Guide
HITRUST certification is a powerful way for healthcare organizations to provide evidence of their security controls. Before starting the certification journey, organizations also need to understand what the process will require from their budget. The costs may differ from one organization to another. Knowing the HITRUST compliance cost before certification can help choose the correct […]
September 3, 2026
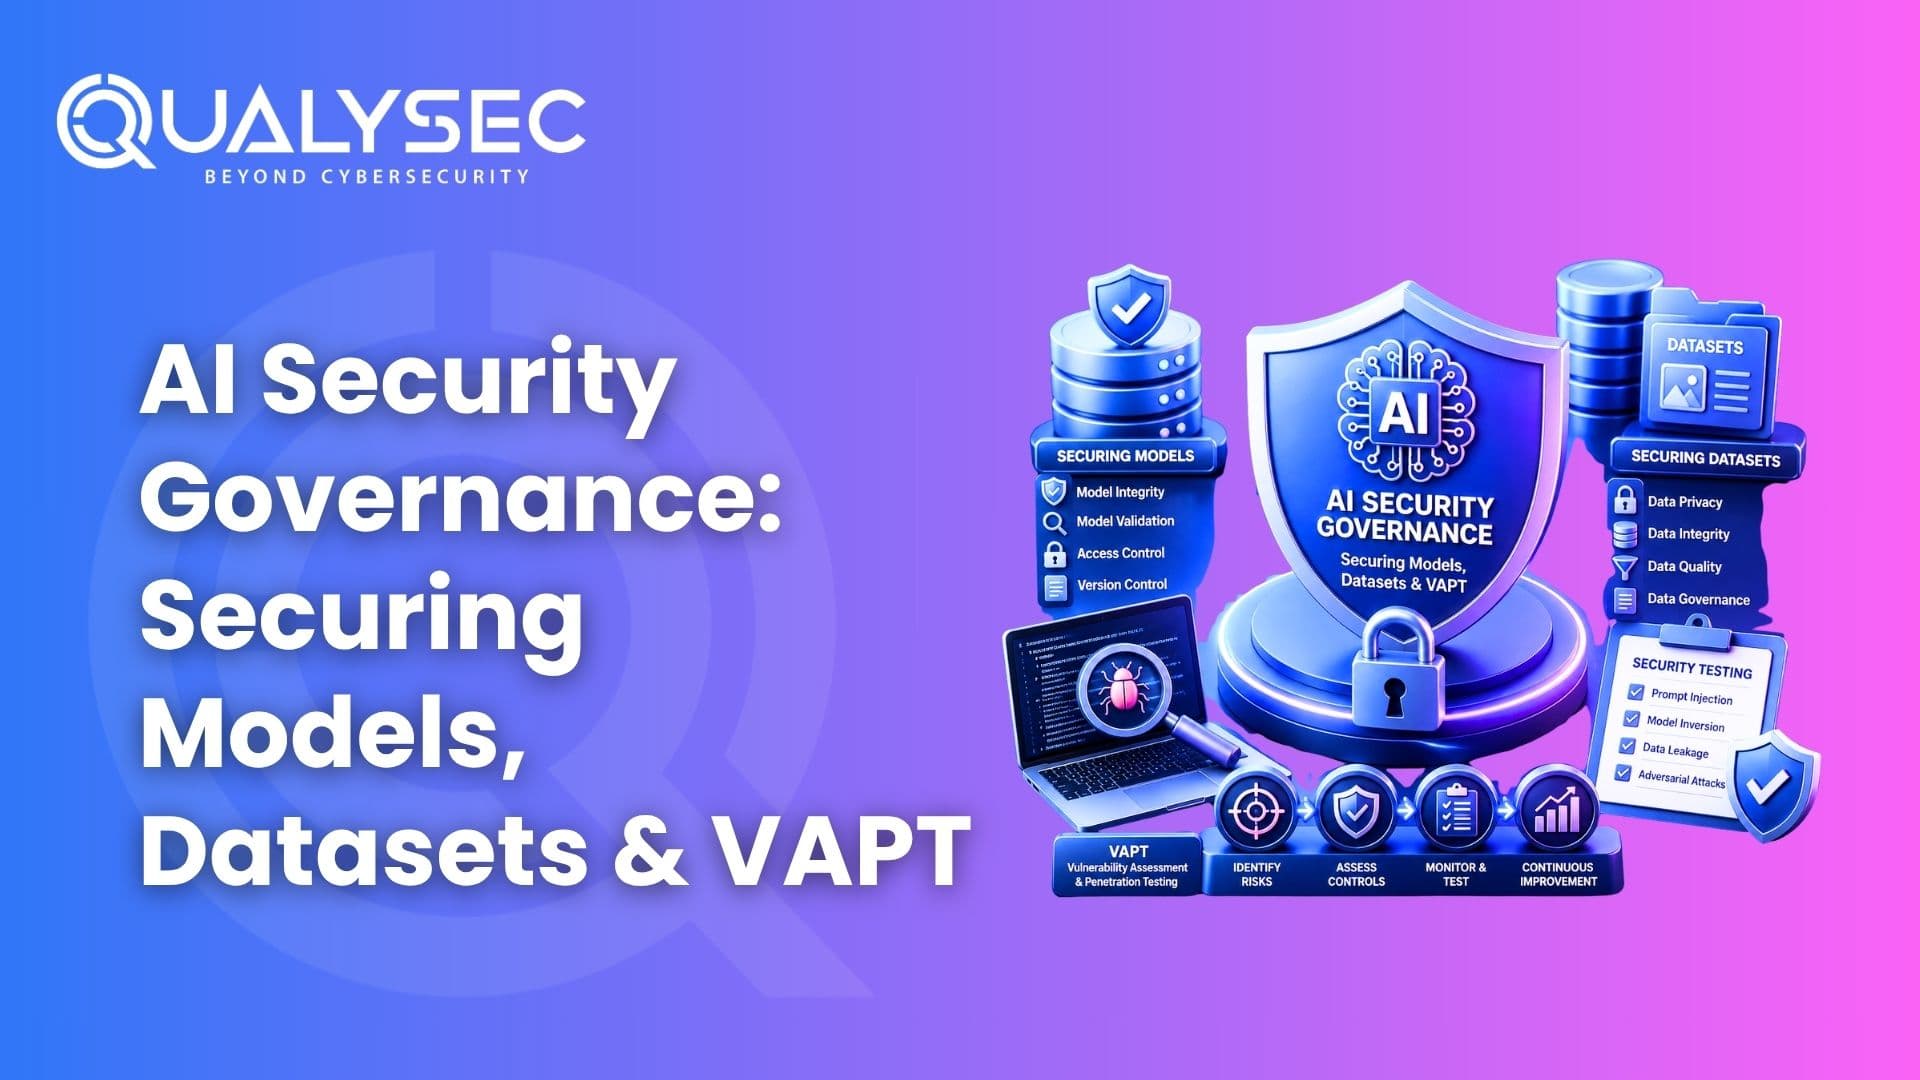
AI Security Governance: Securing Models, Datasets & VAPT
Only 23% of organisations surveyed believe they are prepared to manage AI risk. The remaining three-quarters may have governance gaps they aren’t even aware of. Gartner’s own research on AI TRiSM found that by 2026, at least 80% of unauthorised AI activity inside companies will originate from policy violations and inappropriate use, not external attackers […]
September 2, 2026
Penetration Testing: Australian Compliance Requirements in 2026
When someone asks whether penetration testing is mandatory in Australia, the answer is rarely a simple yes or no. Different organisations answer to different rules. A bank, government agency, SaaS provider, and retail business may all face very different expectations, even when they use similar technology. That distinction matters more as the cost of cybercrime […]
"Don't compromise between depth and speed. Own both. Connect with Swagat, Your trusted penetration testing advisor."

Swagat Kumar Dash
Head Of Business Development